


*.wsf) to deploy an (arbitrary)
AppLocker
policy with a single double-click.
Note: the script requires neither
PowerShell
with its
AppLocker cmdlets
nor
Microsoft Management Console
with its GPEdit.msc and SecPol.msc
snap-ins!
Additionally present a generic AppLocker Policy
(*.xml) for Windows 10 and later versions
plus a
XML Schema Definition
(*.xsd) for validation of AppLocker Policy
files.
Note: Windows 11 22H1 and later versions ship with a pair of identical, active but undocumented hidden DLL and executable rules.
Get-AppLockerFileInformationGet-AppLockerPolicyNew-AppLockerPolicySet-AppLockerPolicyTest-AppLockerPolicySaferCloseLevel()SaferComputeTokenFromLevel()SaferCreateLevel function()SaferGetLevelInformation()SaferGetPolicyInformation()SaferIdentifyLevel()SaferRecordEventLogEntry()SaferSetLevelInformation()SaferSetPolicyInformation()SaferiIsExecutableFileType()*.wsf that sets an
AppLocker
policy on Windows 7 and later versions, then activate
it and finally verify its proper function.
Create a text file *.wsf, for example
AppLocker.wsf, with the following content in an
arbitrary directory:
<?xml version='1.0' encoding='US-ASCII' standalone='yes' ?>
<package>
<comment>Copyright (C) 2009-2026, Stefan Kanthak</comment>
<job>
<object id='Application' progid='Shell.Application' />
<object id='FSO' progid='Scripting.FileSystemObject' />
<reference object='Scripting.FileSystemObject' />
<runtime>
<description>Deploy an AppLocker Policy on Windows 7 and later versions</description>
</runtime>
<script language='JScript'>
if (WScript.Arguments.Length != 0)
WScript.Arguments.ShowUsage()
else
if (FSO.FolderExists(FSO.BuildPath(FSO.GetSpecialFolder(WindowsFolder).Path, 'Sysnative')) == false)
Application.ShellExecute(WScript.FullName, '//Job:Policy ' + WScript.ScriptFullName, WScript.Path, 'RunAs', 1)
else
Application.ShellExecute(FSO.BuildPath(FSO.BuildPath(FSO.GetSpecialFolder(WindowsFolder).Path, 'Sysnative'), FSO.GetFileName(WScript.FullName)), '//Job:Policy ' + WScript.ScriptFullName, FSO.GetSpecialFolder(SystemFolder).Path, 'RunAs', 1)
</script>
</job>
<job id='Policy'>
<object id='AppIdPolicyHandler' classid='clsid:F1ED7D4C-F863-4DE6-A1CA-7253EFDEE1F3' />
<object id='Application' progid='Shell.Application' />
<object id='FSO' progid='Scripting.FileSystemObject' />
<object id='Shell' progid='WScript.Shell' />
<reference guid='85C3F8F7-CFCE-4259-87FF-CAB1F4521F6E' />
<reference object='Scripting.FileSystemObject' />
<reference object='WScript.Shell' />
<resource id='Policy'><![CDATA[<AppLockerPolicy Version='1' />]]></resource>
<runtime />
<script language='JScript'>
if (Application.IsServiceRunning('AppIdSvc') == false)
Application.ServiceStart('AppIdSvc', true)
AppIdPolicyHandler.SetPolicy('', getResource('Policy'))
for (var _ = new Enumerator(FSO.GetSpecialFolder(WindowsFolder).SubFolders); _.atEnd() == false; _.moveNext())
if (FSO.FileExists(FSO.BuildPath(_.item().Path, FSO.GetFileName(WScript.FullName))))
Shell.Run(FSO.BuildPath(_.item().Path, FSO.GetFileName(WScript.FullName)) + ' //Job:Registry ' + WScript.ScriptFullName, WshHide, true)
// WScript.Echo(Shell.Exec(FSO.BuildPath(FSO.GetSpecialFolder(SystemFolder).Path, 'GPUpdate.exe') + ' /Target:Computer').StdOut.ReadAll())
</script>
</job>
<job id='Registry'>
<object id='Shell' progid='WScript.Shell' />
<reference object='WScript.Shell' />
<runtime />
<script language='JScript'>
Shell.RegWrite('HKEY_LOCAL_MACHINE\\SOFTWARE\\Microsoft\\Windows Script Host\\Settings\\IgnoreUserSettings', 1, 'REG_DWORD')
Shell.RegWrite('HKEY_LOCAL_MACHINE\\SOFTWARE\\Microsoft\\Windows Script Host\\Settings\\UseWinSAFER', 1, 'REG_DWORD')
Shell.RegWrite('HKEY_LOCAL_MACHINE\\SOFTWARE\\Policies\\Microsoft\\Internet Explorer\\HTA\\DisableHTMLApplication', 1, 'REG_DWORD')
</script>
</job>
<job id='Validate'>
<object id='Document' progid='MSXML2.DOMDocument.6.0' />
<object id='Schema' progid='MSXML2.XMLSchemaCache.6.0' />
<reference object='MSXML2.DOMDocument.6.0' />
<reference object='MSXML2.XMLSchemaCache.6.0' />
<runtime>
<description>Validate the AppLocker Policy embedded as resource in this Windows Script File</description>
<unnamed helpstring='Mandatory Argument' name='"XML Schema Definition (*.xsd)"' required='1' />
</runtime>
<script language='JScript'>
if (WScript.Arguments.Named.Length != 0
|| WScript.Arguments.Unnamed.Length != 1)
WScript.Arguments.ShowUsage()
else {
Document.async = false
Document.validateOnParse = true
if (Document.load(WScript.ScriptFullName) == false)
WScript.Echo('Error 0x' + (Document.parseError.errorCode >>> 0).toString(16).toUpperCase() + ' at column ' + Document.parseError.linepos + ' in line ' + Document.parseError.line + ' of ' + Document.parseError.url + '\n' + Document.parseError.srcText + '\n' + Document.parseError.reason)
else {
Document.resolveExternals = true
Document.schemas = Schema
Document.schemas.add('', WScript.Arguments.Unnamed.Item(0))
if (Document.loadXML(Document.getElementsByTagName('resource').item(0).text) == false)
WScript.Echo('Error 0x' + (Document.parseError.errorCode >>> 0).toString(16).toUpperCase() + ' at column ' + Document.parseError.linepos + ' in line ' + Document.parseError.line + '\nXPath ' + Document.parseError.errorXPath + '\n\n' + Document.parseError.srcText + '\n\n' + Document.parseError.reason)
else
WScript.Echo(Document.getElementsByTagName('*').length + ' valid XML nodes!')
}
}
</script>
</job>
<job id='Encode'>
<object id='Encoder' progid='Scripting.Encoder' />
<object id='FSO' progid='Scripting.FileSystemObject' />
<reference object='Scripting.Encoder' />
<reference object='Scripting.FileSystemObject' />
<runtime>
<description>Encode this Windows Script File</description>
</runtime>
<script language='JScript'>
if (WScript.Arguments.Length != 0)
WScript.Arguments.ShowUsage()
else {
var Reader = FSO.OpenTextFile(WScript.ScriptFullName, ForReading)
var Script = Reader.ReadAll()
Reader.Close()
var Writer = FSO.OpenTextFile(WScript.ScriptFullName, ForWriting)
Writer.Write(Encoder.EncodeScriptFile('.wsc', Script, 0, ''))
Writer.Close()
}
</script>
</job>
<job id='Sign'>
<object id='Signer' progid='Scripting.Signer' />
<reference object='Scripting.Signer' />
<runtime>
<description>Sign this Windows Script File</description>
<unnamed helpstring='Mandatory Argument' name='"Certificate Name"' required='1' />
</runtime>
<script language='JScript'>
if (WScript.Arguments.Named.Length != 0
|| WScript.Arguments.Unnamed.Length != 1)
WScript.Arguments.ShowUsage()
else
Signer.SignFile(WScript.ScriptFullName, WScript.Arguments.Unnamed.Item(0))
</script>
</job>
<job id='Verify'>
<object id='Signer' progid='Scripting.Signer' />
<reference object='Scripting.Signer' />
<runtime>
<description>Verify the Authenticode Signature of this Windows Script File</description>
</runtime>
<script language='JScript'>
if (WScript.Arguments.Length != 0)
WScript.Arguments.ShowUsage()
else
Signer.VerifyFile(WScript.ScriptFullName, true)
</script>
</job>
</package>getResource()
WScript
WScript.FullName
WScript.Path
WScript.ScriptFullName
WScript.StdOut
WScript.CreateObject()
WScript.Echo()
WScript.Arguments
WScript.Arguments
Item()
WScript.Arguments.Length
WScript.Arguments.Named
WScript.Arguments.Unnamed
WScript.Arguments.ShowUsage()
WScript.Arguments.Named
WScript.Arguments.Named.Item()
WScript.Arguments.Unnamed
WScript.Arguments.Unnamed.Item()
WScript.Shell
Exec()
RegWrite()
Exec
StdOut
Scripting.FileSystemObject
TextStream
ReadAll()
Write()
Scripting.Signer
SignFile()
VerifyFile()
Shell Methods
Shell.IsServiceRunning()
Shell.ServiceStart()
Shell.ShellExecute()
Note: the third job is executed for every processor
architecture – the registry entries it writes enable
SAFER
(either
AppLocker
or
Software Restriction Policies)
for the
Windows Script Host
and prevent to overrule this setting with the opposite value in the
corresponding
Registry
key of any user account.
Note: the policy to disable
HTML Applications
(*.hta) was introduced with security update
5018410
for Windows 10 21H2 respectively security update
5018418
for Windows 11 21H2 and documented in
MSKB
article
5022289.
Replace the highlighted
XML snippet
– an (empty) allow all
AppLocker
policy – with the one you wish to deploy, for example the
generic
AppLocker
policy for Windows 10 and later versions presented
below,
then save the modified Windows Script File
*.wsf.
(Optional) Start the Command Processor
Cmd.exe, then execute the
following command line to
validate
the
AppLocker
policy embedded in step 2. against an external
XML Schema Definition,
for example
%SystemRoot%\Security\ApplicationId\PolicyManagement\AppIdPolicy.xsd
shipped with Windows 7 and later versions, or the one
presented
below:
CSCRIPT.EXE //Job:Validate ‹*.wsf› "%SystemRoot%\Security\ApplicationId\PolicyManagement\AppIdPolicy.xsd"
Microsoft Windows [Version 6.1.7601]
Copyright (c) 2009 Microsoft Corporation. All rights reserved.

Microsoft (R) Windows Script Host Version 5.8
Copyright (C) Microsoft Corporation 1996-2001. All rights reserved.

… valid XML nodes!
CAVEAT:
%SystemRoot%\Security\ApplicationId\PolicyManagement\AppIdPolicy.xsd
has but multiple flaws – it allows decimal
values like −3.14159265358979324 for the Version
attribute of the AppLockerPolicy element,
arbitrary values for the Type
attribute of the RuleCollection element,
invalid
SID Strings
like S-1-000 with no or more than 15 alias
SID_MAX_SUB_AUTHORITIES sub-authorities as well as
S-1-281474976710656-9999999999-4294967296-… with
an authority value greater than 248−1 or with
sub-authority values greater than 232−1 for the
UserOrGroupSid attribute of the
FileHashRule, FilePathRule and
FilePublisherRule elements, reserved
characters like <|> in the Path
attribute of the FilePathCondition element, and
invalid integer values greater than 65535 for all
parts of the HighSection and LowSection
attributes of the BinaryVersionRange element!
(Optional) If you own a code signing certificate run the following command line to sign the Windows Script File modified in step 2.:
CSCRIPT.EXE //Job:Sign ‹*.wsf› "‹certificate name›"
Run the Windows Script File modified in step 2. and optionally signed in step 4. per double-click.
Note: it requires Administrator rights and requests them if necessary via User Account Control.
Restart Windows to activate the just set AppLocker policy.
 Log on to your (unprivileged) standard user account or the so-called
Protected Administrator
account created during
Windows Setup and double-click the
Windows Script File modified in step 2. again to
confirm the successful activation of the
AppLocker
policy for scripts.
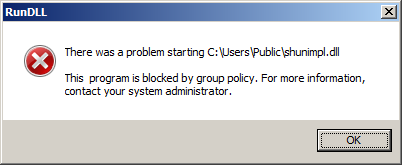 Copy
ShUnimpl.dll
from the system directory
%SystemRoot%\System32\
to the public user directory %PUBLIC%\, then execute
the following command line via the Run
box of the
Start Menu
to confirm the successful activation of the
AppLocker
policy for
DLLs
too:
RunDLL32.exe "%PUBLIC%\ShUnimpl.dll",#0
%SystemRoot%\ and their
Alternate Data Streams.
105763
It uses the well-known groups
S-1-5-113 alias
NT AUTHORITY\Local account and
S-1-5-114
alias
NT AUTHORITY\Local account and member of Administrators group
introduced with security update
2871997
and documented in security advisory
Update to Improve Credentials Protection and Management
instead of S-1-1-0 alias
Everyone respectively
S-1-5-32-544 alias
BUILTIN\Administrators.
Create a text file *.xml, for example
AppLocker.xml, with the following content in an
arbitrary directory:
<?xml version='1.0' encoding='US-ASCII' standalone='yes' ?>
<AppLockerPolicy Version='1'>
<RuleCollection EnforcementMode='Enabled' Type='AppX'>
<FilePublisherRule Action='Allow' Description='Allows members of the "Local Account" group to run digitally signed packaged apps.' Id='a9e18c21-ff8f-43cf-b9fc-db40eed693ba' Name='(MODIFIED Default Rule) All signed packaged apps' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePublisherCondition BinaryName='*' ProductName='*' PublisherName='*'>
<BinaryVersionRange HighSection='*' LowSection='*' />
</FilePublisherCondition>
</Conditions>
<Exceptions>
<FilePublisherCondition BinaryName='*' ProductName='Microsoft.Copilot' PublisherName='CN=Microsoft Corporation, O=Microsoft Corporation, L=Redmond, S=Washington, C=US'>
<BinaryVersionRange HighSection='*' LowSection='*' />
</FilePublisherCondition>
</Exceptions>
</FilePublisherRule>
</RuleCollection>
<RuleCollection EnforcementMode='Enabled' Type='Dll'>
<FilePathRule Action='Allow' Description='Allows members of the "Local Account" group to load DLLs located in the "Program Files" directory.' Id='3737732c-99b7-41d4-9037-9cddfb0de0d0' Name='(MODIFIED Default Rule) All DLLs located in the "Program Files" directory' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePathCondition Path='%PROGRAMFILES%\*' />
</Conditions>
</FilePathRule>
<FilePathRule Action='Allow' Description='Allows members of the "Local Account" group to load DLLs located in the "Windows" directory.' Id='bac4b0bf-6f1b-40e8-8627-8545fa89c8b6' Name='(CORRECTED Default Rule) Microsoft Windows DLLs' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePathCondition Path='%WINDIR%\*' />
</Conditions>
<Exceptions>
<FilePathCondition Path='%SYSTEM32%\Com\Dmp\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp:*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp\*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp:*' />
<FilePathCondition Path='%SYSTEM32%\Tasks\*' />
<FilePathCondition Path='%SYSTEM32%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA\*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA:*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog\*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog:*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons\*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons:*' />
<FilePathCondition Path='%WINDIR%\System32\AppLocker\AppCache.*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys\*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys:*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage\*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers:*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated\*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated:*' />
<FilePathCondition Path='%WINDIR%\System32\WDI\LogFiles\StartupInfo\*' />
<FilePathCondition Path='%WINDIR%\Tasks\*' />
<FilePathCondition Path='%WINDIR%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Temp\*' />
<FilePathCondition Path='%WINDIR%\Temp:*' />
<FilePathCondition Path='%WINDIR%\Tracing\*' />
<FilePathCondition Path='%WINDIR%\Tracing:*' />
</Exceptions>
</FilePathRule>
<FilePathRule Action='Allow' Description='%OSDRIVE%\ProgramData\Microsoft\Windows Defender\Platform (MSKB 4052623)' Id='d2ca0dDc-56af-465f-9c2a-ae5b25d4aa90' Name='MpOAV.dll' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePathCondition Path='%OSDRIVE%\ProgramData\Microsoft\Windows Defender\Platform\*' />
</Conditions>
</FilePathRule>
<FilePathRule Action='Allow' Description='Allows members of the (local) "Administrators" group to load all (protected) DLLs.' Id='fe64f59f-6fca-45e5-a731-0f6715327c38' Name='(MODIFIED Default Rule) All DLLs' UserOrGroupSid='S-1-5-114'>
<Conditions>
<FilePathCondition Path='*' />
</Conditions>
<Exceptions>
<FilePathCondition Path='%OSDRIVE%\Users\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp:*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp\*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp:*' />
<FilePathCondition Path='%SYSTEM32%\Tasks\*' />
<FilePathCondition Path='%SYSTEM32%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA\*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA:*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog\*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog:*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons\*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons:*' />
<FilePathCondition Path='%WINDIR%\System32\AppLocker\AppCache.*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys\*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys:*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage\*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers:*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated\*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated:*' />
<FilePathCondition Path='%WINDIR%\System32\WDI\LogFiles\StartupInfo\*' />
<FilePathCondition Path='%WINDIR%\Tasks\*' />
<FilePathCondition Path='%WINDIR%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Temp\*' />
<FilePathCondition Path='%WINDIR%\Temp:*' />
<FilePathCondition Path='%WINDIR%\Tracing\*' />
<FilePathCondition Path='%WINDIR%\Tracing:*' />
</Exceptions>
</FilePathRule>
<RuleCollectionExtensions>
<ThresholdExtensions>
<Services EnforcementMode='Enabled' />
</ThresholdExtensions>
<RedstoneExtensions>
<SystemApps Allow='Enabled' />
</RedstoneExtensions>
</RuleCollectionExtensions>
</RuleCollection>
<RuleCollection EnforcementMode='Enabled' Type='Exe'>
<FilePathRule Action='Allow' Description='Allows members of the "Local Account" group to run applications located in the "Program Files" directory.' Id='921cc481-6e17-4653-8f75-050b80acca20' Name='(MODIFIED Default Rule) All files located in the "Program Files" directory' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePathCondition Path='%PROGRAMFILES%\*' />
</Conditions>
</FilePathRule>
<FilePathRule Action='Allow' Description='Allows members of the "Local Account" group to run applications located in the "Windows" directory.' Id='a61c8b2c-a319-4cd0-9690-d2177cad7b51' Name='(CORRECTED Default Rule) All files located in the "Windows" directory' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePathCondition Path='%WINDIR%\*' />
</Conditions>
<Exceptions>
<FilePathCondition Path='%SYSTEM32%\Com\Dmp\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp:*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp\*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp:*' />
<FilePathCondition Path='%SYSTEM32%\Tasks\*' />
<FilePathCondition Path='%SYSTEM32%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA\*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA:*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog\*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog:*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons\*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons:*' />
<FilePathCondition Path='%WINDIR%\System32\AppLocker\AppCache.*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys\*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys:*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage\*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers:*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated\*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated:*' />
<FilePathCondition Path='%WINDIR%\System32\WDI\LogFiles\StartupInfo\*' />
<FilePathCondition Path='%WINDIR%\Tasks\*' />
<FilePathCondition Path='%WINDIR%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Temp\*' />
<FilePathCondition Path='%WINDIR%\Temp:*' />
<FilePathCondition Path='%WINDIR%\Tracing\*' />
<FilePathCondition Path='%WINDIR%\Tracing:*' />
</Exceptions>
</FilePathRule>
<FilePathRule Action='Allow' Description='Allows members of the (local) "Administrators" group to run all (protected) applications.' Id='fd686d83-a829-4351-8ff4-27c7de5755d2' Name='(MODIFIED Default Rule) All files' UserOrGroupSid='S-1-5-114'>
<Conditions>
<FilePathCondition Path='*' />
</Conditions>
<Exceptions>
<FilePathCondition Path='%OSDRIVE%\Users\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp:*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp\*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp:*' />
<FilePathCondition Path='%SYSTEM32%\Tasks\*' />
<FilePathCondition Path='%SYSTEM32%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA\*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA:*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog\*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog:*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons\*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons:*' />
<FilePathCondition Path='%WINDIR%\System32\AppLocker\AppCache.*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys\*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys:*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage\*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers:*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated\*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated:*' />
<FilePathCondition Path='%WINDIR%\System32\WDI\LogFiles\StartupInfo\*' />
<FilePathCondition Path='%WINDIR%\Tasks\*' />
<FilePathCondition Path='%WINDIR%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Temp\*' />
<FilePathCondition Path='%WINDIR%\Temp:*' />
<FilePathCondition Path='%WINDIR%\Tracing\*' />
<FilePathCondition Path='%WINDIR%\Tracing:*' />
</Exceptions>
</FilePathRule>
<FilePublisherRule Action='Deny' Description='' Id='ef69c6b9-1e05-40a2-a245-55f6967b337f' Name='Microsoft Copilot' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePublisherCondition BinaryName='*' ProductName='Microsoft.Copilot' PublisherName='CN=Microsoft Corporation, O=Microsoft Corporation, L=Redmond, S=Washington, C=US'>
<BinaryVersionRange HighSection='*' LowSection='*' />
</FilePublisherCondition>
</Conditions>
</FilePublisherRule>
<RuleCollectionExtensions>
<ThresholdExtensions>
<Services EnforcementMode='Enabled' />
</ThresholdExtensions>
<RedstoneExtensions>
<SystemApps Allow='Enabled' />
</RedstoneExtensions>
</RuleCollectionExtensions>
</RuleCollection>
<RuleCollection EnforcementMode='Enabled' Type='Msi'>
<FilePathRule Action='Allow' Description='Allows members of the "Local Account" group to run "Windows Installer" files located in the "Windows\Installer" directory.' Id='5b290184-345a-4453-b184-45305f6d9a54' Name='(MODIFIED Default Rule) All "Windows Installer" files located in the "Windows\Installer" directory' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePathCondition Path='%WINDIR%\Installer\*' />
</Conditions>
</FilePathRule>
<FilePathRule Action='Allow' Description='Allows members of the (local) "Administrators" group to run all (protected) "Windows Installer" files.' Id='64ad46ff-0d71-4fa0-a30b-3f3d30c5433d' Name='(MODIFIED Default Rule) All "Windows Installer" files' UserOrGroupSid='S-1-5-114'>
<Conditions>
<FilePathCondition Path='*' />
</Conditions>
<Exceptions>
<FilePathCondition Path='%OSDRIVE%\Users\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp:*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp\*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp:*' />
<FilePathCondition Path='%SYSTEM32%\Tasks\*' />
<FilePathCondition Path='%SYSTEM32%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA\*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA:*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog\*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog:*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons\*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons:*' />
<FilePathCondition Path='%WINDIR%\System32\AppLocker\AppCache.*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys\*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys:*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage\*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers:*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated\*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated:*' />
<FilePathCondition Path='%WINDIR%\System32\WDI\LogFiles\StartupInfo\*' />
<FilePathCondition Path='%WINDIR%\Tasks\*' />
<FilePathCondition Path='%WINDIR%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Temp\*' />
<FilePathCondition Path='%WINDIR%\Temp:*' />
<FilePathCondition Path='%WINDIR%\Tracing\*' />
<FilePathCondition Path='%WINDIR%\Tracing:*' />
</Exceptions>
</FilePathRule>
<FilePublisherRule Action='Allow' Description='Allows members of the "Local Account" group to run digitally signed "Windows Installer" files.' Id='b7af7102-efde-4369-8a89-7a6a392d1473' Name='(MODIFIED Default Rule) All digitally signed "Windows Installer" files' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePublisherCondition BinaryName='*' ProductName='*' PublisherName='*'>
<BinaryVersionRange HighSection='*' LowSection='*' />
</FilePublisherCondition>
</Conditions>
</FilePublisherRule>
</RuleCollection>
<RuleCollection EnforcementMode='Enabled' Type='Script'>
<FilePathRule Action='Allow' Description='Allows members of the "Local Account" group to run scripts located in the "Program Files" directory.' Id='06dce67b-934c-454f-a263-2515c8796a5d' Name='(MODIFIED Default Rule) All scripts located in the "Program Files" directory' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePathCondition Path='%PROGRAMFILES%\*' />
</Conditions>
</FilePathRule>
<FilePathRule Action='Allow' Description='Allows members of the "Local Account" group to run scripts located in the "Windows" directory.' Id='9428c672-5fc3-47f4-808a-a0011f36dd2c' Name='(CORRECTED Default Rule) All scripts located in the "Windows" directory' UserOrGroupSid='S-1-5-113'>
<Conditions>
<FilePathCondition Path='%WINDIR%\*' />
</Conditions>
<Exceptions>
<FilePathCondition Path='%SYSTEM32%\Com\Dmp\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp:*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp\*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp:*' />
<FilePathCondition Path='%SYSTEM32%\Tasks\*' />
<FilePathCondition Path='%SYSTEM32%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA\*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA:*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog\*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog:*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons\*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons:*' />
<FilePathCondition Path='%WINDIR%\System32\AppLocker\AppCache.*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys\*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys:*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage\*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers:*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated\*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated:*' />
<FilePathCondition Path='%WINDIR%\System32\WDI\LogFiles\StartupInfo\*' />
<FilePathCondition Path='%WINDIR%\Tasks\*' />
<FilePathCondition Path='%WINDIR%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Temp\*' />
<FilePathCondition Path='%WINDIR%\Temp:*' />
<FilePathCondition Path='%WINDIR%\Tracing\*' />
<FilePathCondition Path='%WINDIR%\Tracing:*' />
</Exceptions>
</FilePathRule>
<FilePathRule Action='Allow' Description='Allows members of the (local) "Administrators" group to run all (protected) scripts.' Id='ed97d0cb-15ff-430f-b82c-8d7832957725' Name='(MODIFIED Default Rule) All scripts' UserOrGroupSid='S-1-5-114'>
<Conditions>
<FilePathCondition Path='*' />
</Conditions>
<Exceptions>
<FilePathCondition Path='%OSDRIVE%\Users\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp\*' />
<FilePathCondition Path='%SYSTEM32%\Com\Dmp:*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp\*' />
<FilePathCondition Path='%SYSTEM32%\FxsTmp:*' />
<FilePathCondition Path='%SYSTEM32%\Tasks\*' />
<FilePathCondition Path='%SYSTEM32%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA\*' />
<FilePathCondition Path='%WINDIR%\Debug\WIA:*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog\*' />
<FilePathCondition Path='%WINDIR%\Registration\CRMLog:*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons\*' />
<FilePathCondition Path='%WINDIR%\ServiceProfiles\LocalService\AppData\Local\Microsoft\DLNA\DeviceIcons:*' />
<FilePathCondition Path='%WINDIR%\System32\AppLocker\AppCache.*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys\*' />
<FilePathCondition Path='%WINDIR%\System32\Microsoft\Crypto\RSA\MachineKeys:*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage\*' />
<FilePathCondition Path='%WINDIR%\System32\MSMQ\Storage:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Drivers\Color:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Printers:*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers\*' />
<FilePathCondition Path='%WINDIR%\System32\Spool\Servers:*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated\*' />
<FilePathCondition Path='%WINDIR%\System32\Tasks_Migrated:*' />
<FilePathCondition Path='%WINDIR%\System32\WDI\LogFiles\StartupInfo\*' />
<FilePathCondition Path='%WINDIR%\Tasks\*' />
<FilePathCondition Path='%WINDIR%\Tasks:*' />
<FilePathCondition Path='%WINDIR%\Temp\*' />
<FilePathCondition Path='%WINDIR%\Temp:*' />
<FilePathCondition Path='%WINDIR%\Tracing\*' />
<FilePathCondition Path='%WINDIR%\Tracing:*' />
</Exceptions>
</FilePathRule>
</RuleCollection>
</AppLockerPolicy>Execute the following command lines to apply this AppLocker policy file and enable it:
PowerShell.exe /Command "Set-AppLockerPolicy -XMLPolicy 'AppLocker.xml'"
GPUpdate.exe /Force /Target:Computer
Using the AppLocker Windows PowerShell Cmdlets
Set-AppLockerPolicy
Refresh an AppLocker Policy
%SystemRoot%\Security\ApplicationId\PolicyManagement\AppIdPolicy.xsd
shipped with Windows 7 and later versions!
Create a text file *.xsd, for example
AppLocker.xsd, with the following content next to the
Windows Script File
AppLocker.wsf created
above:
<?xml version='1.0' encoding='US-ASCII' standalone='yes' ?>
<!-- Copyright (C) 2011-2026, Stefan Kanthak -->
<xs:schema attributeFormDefault='unqualified'
elementFormDefault='unqualified'
version='1.0'
xmlns:xs='http://www.w3.org/2001/XMLSchema'
xmlns:xsd='http://www.w3.org/2001/XMLSchema-datatypes'
xmlns:xsi='http://www.w3.org/2001/XMLSchema-instance'>
<xs:annotation>
<xs:documentation>AppLocker Policy XML Schema Definition</xs:documentation>
</xs:annotation>
<xs:element name='AppLockerPolicy'>
<xs:complexType>
<xs:sequence>
<xs:element minOccurs='0'
ref='PolicyExtensions' />
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='RuleCollection' />
</xs:sequence>
<xs:attribute fixed='1'
name='Version'
type='xs:string'
use='required' />
</xs:complexType>
<xs:unique name='RuleCollectionTypeConstraint'>
<xs:selector xpath='RuleCollection' />
<xs:field xpath='@Type' />
</xs:unique>
<xs:unique name='RuleIdConstraint'>
<xs:selector xpath='RuleCollection/*' />
<xs:field xpath='@Id' />
</xs:unique>
</xs:element>
<xs:element name='PolicyExtensions'>
<xs:complexType>
<xs:sequence>
<xs:element name='ThresholdExtensions'>
<xs:complexType>
<xs:sequence>
<xs:element minOccurs='0'
name='Plugins'>
<xs:complexType>
<xs:sequence>
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='Plugin' />
</xs:sequence>
</xs:complexType>
</xs:element>
</xs:sequence>
</xs:complexType>
</xs:element>
</xs:sequence>
</xs:complexType>
</xs:element>
<xs:element name='Plugin'>
<xs:complexType>
<xs:sequence>
<xs:element name='ExecutionCategories'>
<xs:complexType>
<xs:sequence>
<xs:element maxOccurs='unbounded'
ref='ExecutionCategory' />
</xs:sequence>
</xs:complexType>
</xs:element>
</xs:sequence>
<xs:attribute name='Id'
type='uuid' />
<xs:attribute name='Name'
type='xs:string' />
</xs:complexType>
</xs:element>
<xs:element name='ExecutionCategory'>
<xs:complexType>
<xs:sequence>
<xs:element minOccurs='0'
name='Policies'>
<xs:complexType>
<xs:sequence>
<xs:element maxOccurs='unbounded'
minOccurs='0'
name='Policy'>
<xs:complexType>
<xs:attribute name='Id'
type='uuid' />
</xs:complexType>
</xs:element>
</xs:sequence>
</xs:complexType>
</xs:element>
</xs:sequence>
<xs:attribute name='AppidTypes'
use='optional'>
<xs:simpleType>
<xs:list>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:enumeration value='Hash' />
<xs:enumeration value='Path' />
<xs:enumeration value='Publisher' />
</xs:restriction>
</xs:simpleType>
</xs:list>
</xs:simpleType>
</xs:attribute>
<xs:attribute name='Id'
type='uuid' />
</xs:complexType>
</xs:element>
<xs:element name='RuleCollection'>
<xs:complexType>
<xs:sequence>
<xs:choice maxOccurs='unbounded'
minOccurs='0'>
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FileHashRule' />
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FilePathRule' />
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FilePublisherRule' />
</xs:choice>
<xs:element minOccurs='0'
ref='RuleCollectionExtensions' />
</xs:sequence>
<xs:attribute name='EnforcementMode'
use='optional'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:enumeration value='AuditOnly' />
<xs:enumeration value='Enabled' />
<xs:enumeration value='NotConfigured' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
<xs:attribute name='Type'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:enumeration value='AppX' />
<xs:enumeration value='Dll' />
<xs:enumeration value='Exe' />
<xs:enumeration value='Msi' />
<xs:enumeration value='Script' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
</xs:complexType>
</xs:element>
<xs:attributeGroup name='RuleAttributes'>
<xs:attribute name='Action'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:enumeration value='Allow' />
<xs:enumeration value='Deny' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
<xs:attribute name='Description'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:maxLength value='1024' />
<xs:minLength value='0' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
<xs:attribute name='Id'
type='uuid'
use='required' />
<xs:attribute name='Name'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:maxLength value='1024' />
<xs:minLength value='1' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
<xs:attribute name='UserOrGroupSid'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:pattern value='S-1-(0[Xx][0-9A-Fa-f]{1,12}|0|[1-9][0-9]{0,13}|1[0-9]{14}|2[0-7][0-9]{13}|280[0-9]{12}|281[0-3][0-9]{11}|2814[0-6][0-9]{10}|28147[0-3][0-9]{9}|281474[0-8][0-9]{8}|2814749[0-6][0-9]{7}|28147497[0-5][0-9]{6}|281474976[0-6][0-9]{5}|28147497670[0-9]{4}|281474976710[0-5][0-9]{2}|2814749767106[0-4][0-9]|28147497671065[0-6])(-(0[Xx][0-9A-Fa-f]{1,8}|0|[1-9][0-9]{0,8}|[123][0-9]{9}|4[01][0-9]{8}|42[0-8][0-9]{7}|429[0-3][0-9]{6}|4294[0-8][0-9]{5}|42949[0-5][0-9]{4}|429496[0-6][0-9]{3}|4294967[01][0-9]{2}|42949672[0-8][0-9]|429496729[0-5])){1,15}' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
</xs:attributeGroup>
<xs:element name='FileHashRule'>
<xs:complexType>
<xs:all>
<xs:element name='Conditions'>
<xs:complexType>
<xs:sequence>
<xs:element ref='FileHashCondition' />
</xs:sequence>
</xs:complexType>
</xs:element>
</xs:all>
<xs:attributeGroup ref='RuleAttributes' />
</xs:complexType>
</xs:element>
<xs:element name='FileHashCondition'>
<xs:complexType>
<xs:sequence>
<xs:element maxOccurs='unbounded'
name='FileHash'>
<xs:complexType>
<xs:attribute name='Data'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:pattern value='0[Xx]([0-9A-Fa-f]{40}|[0-9A-Fa-f]{64})' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
<xs:attribute name='SourceFileLength'
type='xs:integer'
use='optional' />
<xs:attribute name='SourceFileName'
type='xs:string'
use='optional' />
<xs:attribute name='Type'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:enumeration value='SHA1' />
<xs:enumeration value='SHA256' />
<xs:enumeration value='SHA256Flat' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
</xs:complexType>
</xs:element>
</xs:sequence>
</xs:complexType>
</xs:element>
<xs:element name='FilePathRule'>
<xs:complexType>
<xs:all>
<xs:element name='Conditions'>
<xs:complexType>
<xs:sequence>
<xs:element ref='FilePathCondition' />
</xs:sequence>
</xs:complexType>
</xs:element>
<xs:element minOccurs='0'
name='Exceptions'>
<xs:complexType>
<xs:sequence>
<xs:choice maxOccurs='unbounded'
minOccurs='0'>
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FileHashCondition' />
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FilePathCondition' />
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FilePublisherCondition' />
</xs:choice>
</xs:sequence>
</xs:complexType>
</xs:element>
</xs:all>
<xs:attributeGroup ref='RuleAttributes' />
</xs:complexType>
</xs:element>
<xs:element name='FilePathCondition'>
<xs:complexType>
<xs:attribute name='Path'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:pattern value='[^\a\b\t\n\v\f\r"<>|]{1,32767}' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
</xs:complexType>
</xs:element>
<xs:element name='FilePublisherRule'>
<xs:complexType>
<xs:all>
<xs:element name='Conditions'>
<xs:complexType>
<xs:sequence>
<xs:element ref='FilePublisherCondition' />
</xs:sequence>
</xs:complexType>
</xs:element>
<xs:element minOccurs='0'
name='Exceptions'>
<xs:complexType>
<xs:sequence>
<xs:choice maxOccurs='unbounded'
minOccurs='0'>
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FileHashCondition' />
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FilePathCondition' />
<xs:element maxOccurs='unbounded'
minOccurs='0'
ref='FilePublisherCondition' />
</xs:choice>
</xs:sequence>
</xs:complexType>
</xs:element>
</xs:all>
<xs:attributeGroup ref='RuleAttributes' />
</xs:complexType>
</xs:element>
<xs:element name='FilePublisherCondition'>
<xs:complexType>
<xs:all>
<xs:element name='BinaryVersionRange'>
<xs:complexType>
<xs:attribute name='HighSection'
type='version'
use='required' />
<xs:attribute name='LowSection'
type='version'
use='required' />
</xs:complexType>
</xs:element>
</xs:all>
<xs:attribute name='BinaryName'
type='xs:string'
use='required' />
<xs:attribute name='ProductName'
type='xs:string'
use='required' />
<xs:attribute name='PublisherName'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:minLength value='1' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
</xs:complexType>
</xs:element>
<xs:simpleType name='version'>
<xs:restriction base='xs:string'>
<xs:pattern value='\*|([0-9]{1,4}|[1-5][0-9]{4}|6[0-4][0-9]{3}|65[0-4][0-9]{2}|655[0-2][0-9]|6553[0-5])(\.([0-9]{1,4}|[1-5][0-9]{4}|6[0-4][0-9]{3}|65[0-4][0-9]{2}|655[0-2][0-9]|6553[0-5])){3}' />
</xs:restriction>
</xs:simpleType>
<xs:element name='RuleCollectionExtensions'>
<xs:complexType>
<xs:sequence>
<xs:element ref='ThresholdExtensions' />
<xs:element minOccurs='0'
ref='RedstoneExtensions' />
</xs:sequence>
</xs:complexType>
</xs:element>
<xs:element name='RedstoneExtensions'>
<xs:complexType>
<xs:sequence>
<xs:element minOccurs='0'
name='OriginDataRevocation'>
<xs:complexType>
<xs:attribute name='CurrentOriginDataId'
type='xs:unsignedInt'
use='required' />
<xs:attribute name='TrustedOriginDataId'
type='xs:unsignedInt'
use='required' />
</xs:complexType>
</xs:element>
<xs:element minOccurs='0'
name='SystemApps'>
<xs:complexType>
<xs:attribute name='Allow'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:enumeration value='Enabled' />
<xs:enumeration value='NotEnabled' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
</xs:complexType>
</xs:element>
</xs:sequence>
</xs:complexType>
</xs:element>
<xs:element name='ThresholdExtensions'>
<xs:complexType>
<xs:sequence>
<xs:element minOccurs='0'
name='Services'>
<xs:complexType>
<xs:attribute name='EnforcementMode'
use='required'>
<xs:simpleType>
<xs:restriction base='xs:string'>
<xs:enumeration value='Enabled' />
<xs:enumeration value='NotConfigured' />
<xs:enumeration value='ServicesOnly' />
</xs:restriction>
</xs:simpleType>
</xs:attribute>
</xs:complexType>
</xs:element>
</xs:sequence>
</xs:complexType>
</xs:element>
<xs:simpleType name='uuid'>
<xs:restriction base='xs:string'>
<xs:pattern value='[0-9A-Fa-f]{8}(-[0-9A-Fa-f]{4}){3}-[0-9A-Fa-f]{12}' />
</xs:restriction>
</xs:simpleType>
</xs:schema> Create the text file AppLocker.xml with the following
content in an arbitrary directory:
<?xml version='1.0' standalone='yes' ?>
<!-- Copyright (C) 2011-2026, Stefan Kanthak -->
<Task version='1.2' xmlns='http://schemas.microsoft.com/windows/2004/02/mit/task'>
<Actions Context='Author'>
<ShowMessage>
<Body>Event: $(eventID)
File: $(eventFilePath)
Provider: $(eventProvider)
Time: $(eventTime)
User: $(eventUser)
UserID: $(eventUserID)</Body>
<Title>AppLocker</Title>
</ShowMessage>
</Actions>
<Principals>
<Principal id='Author'>
<GroupId>S-1-5-4</GroupId>
<RunLevel>LeastPrivilege</RunLevel>
</Principal>
</Principals>
<RegistrationInfo>
<Author>Stefan Kanthak</Author>
<Date>2011-04-27T12:34:56.6789</Date>
<Description>Display a message box to the interactive user when 'AppLocker' writes an entry to the event log</Description>
<URI>https://skanthak.hier-im-netz.de/applocker.html</URI>
<Version>0.8.15</Version>
</RegistrationInfo>
<Settings>
<AllowHardTerminate>true</AllowHardTerminate>
<AllowStartOnDemand>false</AllowStartOnDemand>
<DisallowStartIfOnBatteries>false</DisallowStartIfOnBatteries>
<DisallowStartOnRemoteAppSession>false</DisallowStartOnRemoteAppSession>
<Enabled>true</Enabled>
<ExecutionTimeLimit>PT1H</ExecutionTimeLimit>
<Hidden>false</Hidden>
<IdleSettings>
<Duration>PT5M</Duration>
<RestartOnIdle>false</RestartOnIdle>
<StopOnIdleEnd>true</StopOnIdleEnd>
<WaitTimeout>PT1H</WaitTimeout>
</IdleSettings>
<MultipleInstancesPolicy>Queue</MultipleInstancesPolicy>
<Priority>7</Priority>
<RunOnlyIfIdle>false</RunOnlyIfIdle>
<RunOnlyIfNetworkAvailable>false</RunOnlyIfNetworkAvailable>
<StartWhenAvailable>false</StartWhenAvailable>
<StopIfGoingOnBatteries>false</StopIfGoingOnBatteries>
<UseUnifiedSchedulingEngine>false</UseUnifiedSchedulingEngine>
<WakeToRun>false</WakeToRun>
</Settings>
<Triggers>
<EventTrigger>
<Enabled>true</Enabled>
<Subscription><QueryList><Query Id='0' Path='Microsoft-Windows-AppLocker/EXE and DLL'><Select Path='Microsoft-Windows-AppLocker/EXE and DLL'>Event[System[Provider[@Name='Microsoft-Windows-AppLocker'] and (Level=1 or Level=2 or Level=3)]]</Select><Select Path='Microsoft-Windows-AppLocker/MSI and Script'>Event[System[Provider[@Name='Microsoft-Windows-AppLocker'] and (Level=1 or Level=2 or Level=3)]]</Select></Query></QueryList></Subscription>
<ValueQueries>
<Value name='eventChannel'>Event/System/Channel</Value>
<Value name='eventComputer'>Event/System/Computer</Value>
<Value name='eventCorrelation'>Event/System/Correlation</Value>
<Value name='eventFilePath'>Event/UserData/RuleAndFileData/FilePath</Value>
<Value name='eventID'>Event/System/EventID</Value>
<Value name='eventKeywords'>Event/System/Keywords</Value>
<Value name='eventLevel'>Event/System/Level</Value>
<Value name='eventOpcode'>Event/System/Opcode</Value>
<Value name='eventProcessID'>Event/System/Execution/@ProcessID</Value>
<Value name='eventProvider'>Event/System/Provider/@Name</Value>
<Value name='eventRecordID'>Event/System/EventRecordID</Value>
<Value name='eventTask'>Event/System/Task</Value>
<Value name='eventThreadID'>Event/System/Execution/@ThreadID</Value>
<Value name='eventTime'>Event/System/TimeCreated/@SystemTime</Value>
<Value name='eventUser'>Event/UserData/RuleAndFileData/TargetUser</Value>
<Value name='eventUserID'>Event/System/Security/@UserID</Value>
<Value name='eventVersion'>Event/System/Version</Value>
</ValueQueries>
</EventTrigger>
</Triggers>
</Task> Create a Scheduled Task from the task definition file
AppLocker.xml created in step 1.:
SCHTASKS.EXE /CREATE /TN "AppLocker Alert" /XML AppLocker.xmlSchtasks.exe
SUCCESS: The scheduled task "AppLocker Alert" has successfully been created.
Use the X.509 certificate to send S/MIME encrypted mail.
Note: email in weird format and without a proper sender name is likely to be discarded!
I dislike
HTML (and even
weirder formats too) in email, I prefer to receive plain text.
I also expect to see your full (real) name as sender, not your
nickname.
I abhor top posts and expect inline quotes in replies.
as iswithout any warranty, neither express nor implied.
cookiesin the web browser.
The web service is operated and provided by
Telekom Deutschland GmbH The web service provider stores a session cookie
in the web
browser and records every visit of this web site with the following
data in an access log on their server(s):